Selecting the right MCP gateway for enterprise AI deployment requires evaluating security features, deployment speed, compliance posture, and governance capabilities. Mintive (formerly MintMCP), TrueFoundry, and RunLayer each approach the Model Context Protocol (MCP) infrastructure challenge differently, serving distinct organizational needs. Mintive's MCP Gateway focuses on data-permissions-first deployment with SOC 2 Type II audited controls, OAuth brokering, and tool-level governance. TrueFoundry operates as a unified MLOps platform with MCP gateway capabilities alongside model serving. RunLayer emphasizes MCP-specific security with threat detection features. This comparison examines all three platforms to help engineering leaders determine which approach aligns with their enterprise AI governance priorities.
Key Takeaways
- Mintive provides hosted MCP connectors run by Mintive, OAuth brokering for stdio and hosted MCP servers, and managed deployment for production MCP access
- Mintive is listed in the Cursor Hooks Partners Program, supporting AI coding governance workflows
- TrueFoundry offers a unified MLOps platform with LLM gateway access to multiple model providers, while gateway performance depends on deployment configuration and workload
- RunLayer provides a curated MCP catalog with MCP-specific threat detection capabilities
- Mintive's Virtual MCP Bundles enable per-use-case endpoints with SCIM-driven membership, tool curation, and policy controls
- All three platforms support enterprise authentication and identity integrations
Understanding the Landscape: Enterprise MCP Deployment Challenges
MCP has emerged as a widely adopted standard for connecting AI clients to enterprise data and tools, with support from Anthropic, OpenAI, Google, and Microsoft. According to NIST's AI Risk Management Framework, proper governance of AI systems requires transparency, accountability, and security controls at every integration point. Yet this adoption brings significant challenges around deployment complexity, security vulnerabilities, and governance gaps.
The Rise of Shadow AI and Its Implications
Organizations face a growing shadow AI problem. Teams adopt AI tools and MCP servers without IT oversight, creating security blind spots and compliance risks. Gartner research on AI governance indicates that ungoverned AI adoption is among the top risks facing enterprises in 2024. Without centralized governance, AI tools operate as black boxes with:
- Zero telemetry into what data agents access
- No request history for audit purposes
- Uncontrolled access to production systems and sensitive files
This ungoverned adoption exposes enterprises to data leakage, credential exposure, and regulatory violations. Engineering leaders need infrastructure that transforms shadow AI into sanctioned AI without disrupting developer workflows.
The Inherent Complexities of MCP Integration
Most MCP servers are STDIO-based, requiring local installation and manual configuration. Deploying these servers at enterprise scale introduces multiple friction points:
- Authentication gaps: STDIO servers typically run without OAuth or SSO protection
- Credential sprawl: API keys and tokens scattered across developer machines
- No audit trails: Tool calls, file access, and bash commands go unmonitored
- Deployment overhead: Days or weeks to move from local development to production
Mintive addresses these challenges through its MCP Gateway architecture, which provides centralized governance, OAuth brokering, hosted MCP connectors, and managed deployment. Understanding how each platform handles these complexities helps identify the right fit for your organization.
Mintive's Approach to Secure and Governed Enterprise AI
Mintive is built for enterprise MCP deployment that is fast, secure, and governed. Every platform feature reflects this data-permissions-first approach.
Managed Deployments and Unified Management
Mintive helps teams move MCP access into production through managed deployment and hosted connector infrastructure. The platform handles:
- Hosted MCP connectors: Mintive runs connector instances with isolated execution, so customers do not need to operate connector runtimes or Kubernetes pods
- OAuth brokering: Authentication support for stdio and hosted MCP servers without requiring each team to manage OAuth complexity on its own
- Central registry: Installation and configuration from a curated connector catalog
- Virtual MCP Bundles: Bundle multiple connectors into per-use-case endpoints with centralized auth, SCIM-driven membership, tool curation, and policy controls
This Virtual MCP approach enables administrators to create role-based endpoints. Each role receives an automatically configured endpoint with appropriate tools, simplifying access management across teams.
Robust Security and Compliance Frameworks
Mintive is SOC 2 Type II audited, compliant with HIPAA standards, penetration tested, and built with audit-ready logging and governance controls that support internal compliance programs. The security architecture includes:
- OAuth 2.0, SAML, and SSO integration for enterprise identity management
- SSO and SCIM-driven RBAC with granular tool permissions by team, group, or agent
- Real-time monitoring through live dashboards for server health and usage patterns
- Centralized governance controls for enterprise deployments
- Data encrypted in transit and at rest with data residency options and uptime SLA support
For organizations with strict regulatory requirements, Mintive's audit-ready documentation and compliance posture reduce the path to production approval.
Extensive Audit Trails for Regulatory Needs
Complete audit trails capture every MCP interaction, access request, and configuration change. These logs support:
- SOC 2 audit requirements
- Internal compliance documentation support
- Data access tracking
- Internal security reviews
The MCP Gateway platform centralizes this observability, giving security teams visibility into what data AI tools access and when.
TrueFoundry's Approach
TrueFoundry takes a different approach, positioning itself as a unified AI platform that includes MCP gateway functionality alongside broader MLOps capabilities. Understanding where each platform excels helps match solutions to specific needs.
LLM Operations and Model Deployment
TrueFoundry provides a comprehensive AI lifecycle platform with:
- LLM gateway with multiple providers: Provider-agnostic routing across OpenAI, Anthropic, and other providers
- Model serving infrastructure: GPU-optimized deployment with vLLM, TGI, and Triton backends
- Agent framework support: Integration with Langgraph, CrewAI, and AutoGen
The platform emphasizes reduced deployment time compared to industry averages. For teams needing end-to-end MLOps alongside MCP governance, this unified approach offers workflow consolidation.
Mintive combines governed MCP tool access with an LLM gateway that connects OpenAI, Anthropic, and Fireworks, so teams can also control model use through per-group budgets and allowed-model lists. Model serving and full MLOps remain outside its scope.
Security and Governance Features
Both Mintive and TrueFoundry maintain enterprise security postures. Mintive's data-permissions-first architecture is built around SSO, SCIM-driven RBAC, tool-level allowlisting, rule-based policy, credential management, and audit logs for AI tool governance. The platform's specialized focus means compliance features are built around MCP-specific risks rather than adapted from general MLOps security models.
Performance and Monitoring Capabilities
TrueFoundry materials describe gateway performance for specific benchmark scenarios, while actual overhead depends on deployment configuration, workload, and traffic patterns.
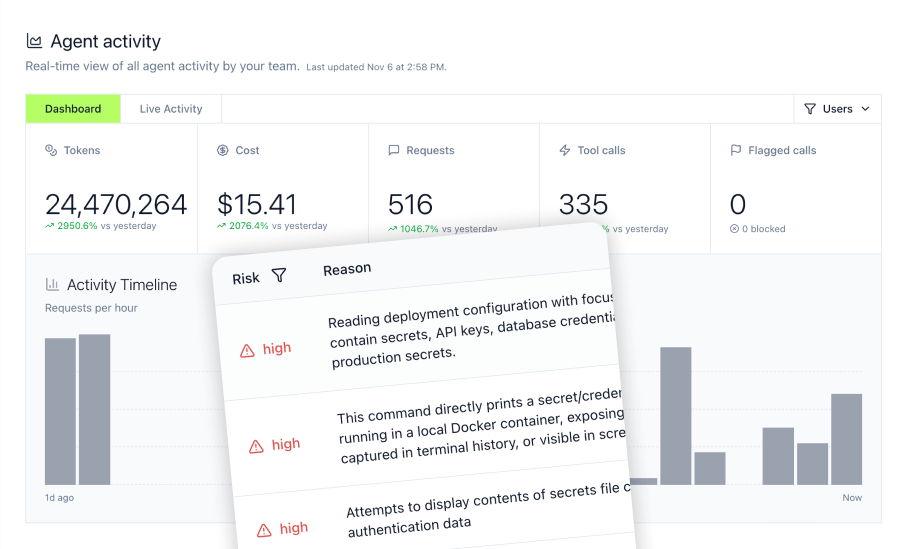
Mintive provides real-time usage tracking with:
- Cost analytics by team, project, and tool
- Performance metrics including response times and error rates
- Data access logs showing exactly what each AI tool accesses
Mintive's LLM gateway shows model-call usage, cost, model, and latency next to tool calls, while Agent Monitor captures coding-agent file access and command activity.
RunLayer's MCP Deployment
RunLayer emphasizes security-first MCP adoption with a curated server catalog and MCP-specific threat detection capabilities.
Deployment and Integration Model
RunLayer provides installs from its server catalog with an enterprise-focused onboarding and governance model. The platform's catalog offers broad compatibility across different use cases and integration needs.
Mintive offers managed MCP deployment through hosted connector infrastructure, OAuth brokering, and isolated connector execution. Organizations needing rapid time-to-value may find Mintive's deployment model well-suited to fast-moving AI initiatives.
AI Client Compatibility
Both platforms support major AI clients. RunLayer supports a range of AI development clients and coding environments.
Mintive provides governance for Claude, Cursor, ChatGPT, Gemini, and Copilot, along with MCP-compatible clients and custom agents. As a Cursor Hooks Partners Program listing, Mintive supports teams using Cursor in enterprise coding workflows.
Access Control and Identity Management
Mintive's self-service model enables developers to request and receive AI tool access quickly while administrators maintain centralized control. Key features include:
- Centralized credentials: All API keys and tokens managed in one place
- Pre-configured policies: Deploy MCP tools without slowing developers
- Team-based access controls: Centralized user provisioning with SSO and SCIM-driven role-based permissions
RunLayer offers fine-grained access control with Okta and Entra ID integration plus SCIM support. Both platforms address enterprise identity management, though Mintive's Virtual MCP Bundles provide unique capabilities for creating per-use-case endpoints with SCIM-driven membership.
Bridging the Gap: Internal Data Integration with AI Agents
Mintive bridges AI assistants like ChatGPT and Claude with internal data and tools. The platform handles authentication, permissions, and audit trails for enterprise data source connections.
Connecting AI to Enterprise Data Sources
Mintive provides purpose-built connectors for common enterprise systems:
Elasticsearch MCP Server enables AI-powered knowledge base search with tools for:
- Query DSL searches for flexible document retrieval
- ES|QL queries for advanced data analysis
- Index listing and field mapping retrieval
- Shard health monitoring
Snowflake MCP Server connects AI agents to data warehouses with:
- Natural language to SQL conversion via Cortex Analyst
- Semantic search against configured Cortex Search services
- SQL query execution with DML and DDL support
- Semantic view querying with dimensions, metrics, and facts
Gmail MCP Server supports secure email integration with:
- Advanced query syntax for email search
- Complete email content retrieval including attachments
- Draft creation and reply generation
- Controlled send workflows
Use Cases Across HR, Product, and Finance Teams
These integrations enable practical AI applications across the organization:
- HR teams: Build AI-accessible knowledge bases from company documentation, policies, and training materials stored in Elasticsearch
- Product teams: Enable AI-powered customer-facing documentation search and contextual help systems
- Finance teams: Automate financial reporting, variance analysis, and forecasting with AI agents accessing Snowflake data models
- Executive teams: Generate real-time business intelligence dashboards from governed data without SQL expertise
Ensuring Secure Data Access for AI Agents
Each connector operates within Mintive's governance framework. Administrators configure:
- Which users can access which data sources
- What operations are permitted through tool-level allowlisting and rule-based policy
- Audit logging for every query and data access event
- Rate limiting and usage controls
This governed approach transforms ad-hoc AI data access into sanctioned, auditable workflows.
Protecting Sensitive Information: Agent Monitor and Security Guardrails
Coding agents operate with extensive system access, reading files, executing commands, and accessing production systems through MCP tools. Mintive's two-layer governance model combines MCP Gateway controls with Agent Monitor visibility for local non-MCP agent activity.
Monitoring Every AI Tool Invocation and Bash Command
Agent Monitor extends visibility beyond MCP traffic to local agent activity in tools such as Cursor and Claude Code. This architecture enables:
- Tool call tracking: Monitor every MCP tool invocation from coding agents
- Bash command monitoring: Track commands executed by AI assistants
- MCP inventory: Complete visibility into installed MCPs across teams
- File access logging: See which files agents access and when
Blocking Risky Operations and Protecting Critical Data
Real-time security guardrails help prevent risky actions before they execute:
- Dangerous command blocking: Stop risky bash commands in real time
- Sensitive file protection: Prevent access to .env files, SSH keys, and credentials
- Environment secret protection: Block tool calls attempting to read secrets
- Permission controls: Configure what MCPs can and cannot do
For organizations concerned about AI agents accessing production credentials or executing destructive commands, these guardrails provide essential safeguards.
Ensuring Auditability for Security and Compliance
Every operation flows through complete audit trails:
- Command history: Full record of bash commands for security review
- Tool call logs: Detailed history of MCP tool invocations
- File access records: Documentation of every file read or modified
- User attribution: Clear mapping of actions to specific users and agents
This audit capability supports security incident investigation, compliance documentation, and operational visibility into AI tool usage patterns.
Cost Efficiency and Observability: Driving ROI in AI Tool Adoption
Enterprise AI adoption requires understanding costs, tracking performance, and demonstrating value. Mintive provides the observability infrastructure to manage AI tool investments effectively.
Tracking Spending and Allocating Costs Precisely
Mintive's cost analytics deliver granular visibility into AI tool spending:
- Team-level tracking: Understand which teams consume the most AI resources
- Project attribution: Allocate costs to specific initiatives for budget management
- Tool-level breakdown: See spending patterns across different MCP servers and AI clients
- Trend analysis: Track spending over time to forecast future needs
Optimizing Performance and Minimizing Errors
Performance metrics help teams optimize AI tool usage:
- Response time monitoring: Measure latency across MCP servers and AI clients
- Error rate tracking: Identify problematic integrations or configurations
- Usage pattern analysis: Understand how teams use AI tools throughout workflows
- SLA compliance monitoring: Ensure AI infrastructure meets availability requirements
Achieving ROI with Managed Enterprise AI
Organizations deploying AI strategically focus on measurable outcomes tied to specific workflows. Mintive's managed infrastructure reduces the operational burden of AI tool deployment, enabling teams to focus on high-value applications rather than infrastructure maintenance.
Choosing Mintive for Enterprise AI Infrastructure
Mintive addresses the core challenges engineering leaders face when deploying MCP at enterprise scale: deployment speed, security posture, compliance requirements, and operational visibility. Its MCP gateway is part of one platform governing both tool calls and model calls, with model-call controls through the LLM gateway.
Key Mintive Differentiators
Mintive differentiates itself through:
- Fast time to production: Move MCP access into production through managed deployment and hosted connector infrastructure
- Secure and compliant architecture: SOC 2 Type II audited, compliant with HIPAA standards, penetration tested, and built with audit-ready logging from day one
- OAuth brokering: Support authentication for stdio and hosted MCP servers without modifying MCP server code
- Virtual MCP Bundles: Per-use-case endpoints with SCIM-driven membership, curated tools, and policy controls
- Agent Bundles: Per-agent identity with M2M auth and an “act as agent” flow
- Cursor Hooks Partners Program listing: Partnership-backed support for teams governing Cursor-based AI coding workflows
Supporting a Wide Range of AI Clients
Mintive works with existing AI tool deployments without requiring workflow changes. Supported clients include:
- Claude
- Cursor
- ChatGPT
- Gemini
- Microsoft Copilot
- Custom MCP-compatible agents
This broad compatibility ensures organizations can standardize on Mintive governance while teams continue using their preferred AI tools.
From Shadow AI to Sanctioned AI
Teams are already using AI tools across organizations. Mintive provides the visibility and control to transform ungoverned adoption into enterprise-ready infrastructure without disrupting developer productivity. Deploy MCP tools with pre-configured policies, gain observability into usage patterns, and meet compliance requirements with complete audit trails.
For engineering leaders evaluating MCP gateway solutions, Mintive offers a fast path from local development to production deployment with the security and governance enterprises require. The platform's data-permissions-first architecture, OAuth brokering, hosted MCP connectors, and Virtual MCP Bundle capabilities address the specific challenges of enterprise AI tool governance. By centralizing credentials, providing real-time monitoring, and maintaining comprehensive audit trails, Mintive transforms shadow AI adoption into sanctioned, governed infrastructure while maintaining developer velocity. Book a demo to see how Mintive can accelerate your enterprise AI infrastructure.
Frequently Asked Questions
What security features does Mintive provide compared to alternatives?
Mintive is SOC 2 Type II audited, compliant with HIPAA standards, penetration tested, and provides OAuth brokering for stdio and hosted MCP servers. The platform includes audit-ready logging, SSO and SCIM-driven RBAC, credential management, and rule-based policy built specifically for AI tool governance. TrueFoundry offers security controls within its broader MLOps platform. RunLayer focuses on MCP-specific threat detection including tool poisoning and command injection prevention. Mintive's specialized focus means security features address MCP-specific risks directly rather than adapting general infrastructure security models.
How does Mintive's deployment compare to alternatives for STDIO-based servers?
Mintive supports production MCP access through hosted connector infrastructure, OAuth brokering, and managed deployment. The platform helps teams avoid operating connector runtimes, Kubernetes pods, and scaling logic themselves. TrueFoundry emphasizes reduced deployment time compared to industry averages. RunLayer provides installs from its catalog with an enterprise-focused onboarding model. For teams prioritizing speed to production, Mintive's deployment model offers a fast path to governed AI tool access.
Can Mintive integrate with existing enterprise data sources?
Yes. Mintive provides purpose-built connectors for enterprise data sources. The Elasticsearch MCP Server enables AI-powered knowledge base search, support ticket intelligence, and log analysis. The Snowflake MCP Server connects AI agents to data warehouses with natural language to SQL conversion, semantic search, and governed query execution. The Gmail MCP Server supports email search, drafting, and controlled send workflows. All connectors operate within Mintive's governance framework with configurable permissions and complete audit trails.
What compliance attestations does Mintive hold?
Mintive is SOC 2 Type II audited, compliant with HIPAA standards, penetration tested, and supports enterprise security reviews through its Trust Center. Its governance controls reduce the path to production approval for regulated industries, provide audit-ready documentation for compliance reviews, and demonstrate enterprise security posture to stakeholders. Complete audit logs capture every MCP interaction, access request, and configuration change, supporting internal compliance documentation requirements.
How does Mintive control costs and provide usage analytics?
Mintive provides real-time usage tracking with cost analytics broken down by team, project, and tool. Performance metrics measure response times, error rates, and usage patterns across all MCP connections. Data access logs show exactly what data each AI tool accesses and when. This observability enables organizations to understand spending patterns, optimize tool usage, allocate costs accurately, and demonstrate ROI from AI infrastructure investments.