Selecting the right MCP gateway for enterprise AI deployments requires evaluating security posture, deployment complexity, compliance readiness, and total cost of ownership. Both Mintive (formerly MintMCP) and Obot MCP Gateway have emerged as notable options in the rapidly expanding MCP infrastructure market, but they serve fundamentally different organizational needs. Mintive's MCP Gateway delivers a managed, data-permissions-first platform with SOC 2 Type II audited security controls, SSO and SCIM-driven RBAC, tool-level policy, audit logs, credential management, and hosted MCP connectors, while Obot provides an open-source, self-hosted solution for teams with Docker and Kubernetes expertise. This comparison examines both platforms across security, deployment, integrations, and cost to help engineering leaders determine which approach aligns with their enterprise requirements.
Key Takeaways
- Deployment model differs significantly: Mintive is managed SaaS-first with US and EU deployment options and VPC/self-hosted options on request, while Obot is OSS-first and self-hosted, with Docker for development and Kubernetes for production
- Mintive provides lower infrastructure overhead as a managed platform, compared to Obot's self-hosted model that requires more dedicated DevOps involvement for ongoing maintenance
- Mintive provides hosted MCP connectors run by Mintive for enterprise systems such as Elasticsearch, Snowflake, and Gmail, while Obot offers a searchable directory with community-contributed servers
- Obot is OSS-first and self-hosted, appealing to organizations with Kubernetes expertise seeking maximum customization and infrastructure control
- Total cost of ownership often favors managed platforms: Building equivalent MCP infrastructure in-house can become expensive once engineering, infrastructure, and compliance work are included
- Mintive centers governance around SSO, SCIM-driven RBAC, Virtual MCP Bundles, tool-level policy, Agent Bundles, and audit logs, while Obot requires more customer-owned configuration and operations depending on deployment
Understanding the Core: What is an MCP Gateway?
The Model Context Protocol (MCP) has become a common open standard for connecting AI assistants like Claude, ChatGPT, and Cursor to enterprise data and tools. MCP adoption has accelerated rapidly across organizations seeking to unlock AI-powered workflows.
An MCP gateway sits between AI clients and MCP servers, providing centralized control over authentication, authorization, monitoring, and governance. Without a gateway, organizations face fragmented security policies, scattered credentials, and zero visibility into what AI agents access.
The Role of MCP in Enterprise AI
MCP solves a fundamental challenge: AI assistants need secure access to internal systems, databases, APIs, documentation, and communication tools, to deliver real business value. Direct connections create security risks. MCP provides a standardized protocol for these connections, but the protocol alone doesn't address enterprise requirements for:
- Authentication and authorization: Ensuring only approved users and agents access specific tools
- Audit trails: Recording every tool invocation for compliance and security review
- Rate limiting and cost control: Preventing runaway API calls and managing expenses
- High availability: Maintaining production SLAs with automatic failover
Gartner's 2025 Software Engineering Survey projects that by 2026, 75% of API gateway vendors will add MCP features, reflecting the protocol's growing enterprise importance.
Key Functions of an MCP Gateway
MCP gateways address three core problems that emerge when scaling AI tool access:
- Tool Organization: Consolidating multiple MCP servers into curated, role-based toolsets
- Protocol Translation: Converting STDIO-based local servers into remotely accessible services
- Security Control: Enforcing enterprise authentication, logging every request, and blocking risky operations
For a deeper exploration of gateway architecture, see the guide on understanding MCP gateways.
Security and Compliance: Ensuring Trustworthy AI Deployments
Security represents the most significant differentiator between Mintive and Obot. Organizations in regulated industries, including healthcare, financial services, and government, require documented security controls before deploying AI tools that access sensitive data.
Enterprise-Grade Authentication and Authorization
Mintive provides enterprise authentication and access governance:
- SSO, SAML, OIDC, and enterprise IdP integration
- SCIM-driven RBAC using IdP groups
- OAuth brokering for stdio and hosted MCP servers
- Virtual MCP Bundles for per-use-case endpoints with curated tools and SCIM-driven membership
- Tool-level allowlisting and rule-based policy
Obot supports enterprise authentication patterns but requires more customer-owned configuration:
- Identity-provider integration depending on deployment and edition
- Docker for development and Kubernetes for production
- Customer-owned deployment and access-control setup
- Manual configuration for comparable gateway policy, runtime, and monitoring workflows
The practical difference: Mintive provides a managed, SSO-fronted remote MCP endpoint with OAuth brokering, Virtual MCP Bundles, and tool-level policy. Obot gives Kubernetes-fluent teams more infrastructure control, but customers operate more of the runtime, configuration, and access-control layer themselves.
Meeting Regulatory Requirements with Audit Trails
Compliance-driven organizations need auditable records of every AI tool interaction. Mintive is SOC 2 Type II audited and provides:
- Complete audit trails of every MCP interaction, access request, and configuration change
- Compliance with HIPAA standards, with HIPAA documentation available on request for customers handling protected health information
- BAAs available for eligible customers
- Continuous compliance monitoring via Drata
- Data encryption in transit and at rest
- Data residency options and uptime SLA details available through Mintive's Trust Center and security review process
Obot records MCP request/response metadata through its MCP Server Shim, but organizations still need to own their broader compliance program, hosting environment, and evidence collection.
Protecting Sensitive Information with Real-time Controls
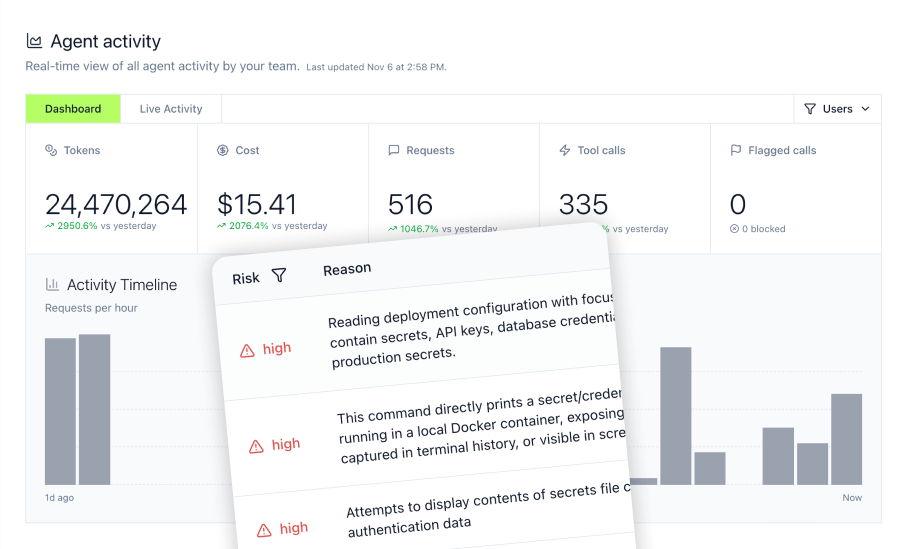
Mintive's Gateway and Agent Monitor provide two-layer governance beyond basic gateway routing:
- Tool-level allowlisting and rule-based policy before execution
- JavaScript Gateway Middleware in a JS sandbox for inline policy, masking, blocking, and external DLP or guardrails integrations
- Complete audit trail of MCP tool calls and local agent activity
- Visibility into bash commands, file reads/writes, prompt submissions, and tool usage from coding agents
- Tool-update policy to prevent silent expansion of upstream MCP server capabilities
This defense-in-depth approach addresses a critical enterprise concern: coding agents like Cursor and Claude Code operate with extensive system access, and without monitoring, organizations cannot see what agents access or control their actions.
Deployment and Management: Ease of Use for Enterprise Scale
Deployment complexity determines how quickly teams can move from evaluation to production and how much ongoing operational burden the platform creates.
Streamlined Server Deployment
Mintive emphasizes managed deployment and centralized administration:
- Managed SaaS-first deployment with US and EU options
- VPC and self-hosted options available on request
- Hosted MCP connectors run by Mintive
- Automatic hosting and lifecycle management for connector runtimes
- Admin MCP for managing rules, connectors, logs, and operations from MCP clients
- No Kubernetes pods, runtimes, or scaling layer for the customer to operate
Obot is designed for self-hosted infrastructure:
- Docker-based development workflow
- Kubernetes-based production deployment
- GitOps workflow support for infrastructure-as-code management
- Full architectural control for platform engineering and DevOps teams
- Composite MCP server creation for combining multiple servers into logical endpoints
For organizations with existing Kubernetes expertise, Obot's approach provides granular control. For teams prioritizing managed deployment and centralized governance, Mintive reduces the infrastructure work required compared to self-hosted alternatives.
Monitoring and Observability for Production Systems
Production AI deployments require visibility into system health, usage patterns, and potential issues.
Mintive provides:
- Centralized observability for MCP traffic and agent activity
- Audit logs for tool calls, access requests, and configuration changes
- Security alert detection and notification
- Performance metrics including response times and error rates
- Cross-client governance for Claude, Cursor, ChatGPT, Gemini, and Copilot
Obot offers:
- Health monitoring for deployed servers
- Kubernetes-native observability integration
- Customer-managed monitoring setup for advanced dashboards
Scalability and High Availability Options
Mintive includes managed platform options:
- Uptime SLA details available through security review
- Managed connector hosting and runtime operations
- US and EU deployment options
- VPC/self-hosted options available on request
Obot provides scalability through Kubernetes:
- Self-managed regional deployment
- Customer-owned failover and scaling configuration
- Full control over scaling policies
- Air-gapped deployment possible for maximum control
Bridging AI with Internal Systems: Integration Capabilities
The value of an MCP gateway depends on which enterprise systems it can connect to AI assistants. Both platforms support the MCP standard, but differ in pre-built connector depth and operational model.
Connecting AI to Your Data Warehouses
Mintive provides hosted MCP connectors for enterprise data systems:
Snowflake MCP Server can support governed AI access to Snowflake workflows through scoped tools, centralized authentication, audit logs, and policy enforcement.
Use cases include:
- Product analytics through governed natural language workflows
- Financial reporting workflows with auditable data access
- Executive business intelligence with controlled tool access
Obot supports Snowflake through community MCP servers but requires additional configuration and customer-managed runtime operations for equivalent deployment and governance.
AI-Powered Knowledge Management
Mintive's Elasticsearch MCP Server supports governed AI access to Elasticsearch-backed knowledge and search workflows with centralized policy, logging, and connector hosting.
Enterprise applications:
- HR teams building AI-accessible knowledge bases from company documentation
- Support teams searching historical tickets for faster resolution
- Product teams enabling AI-powered documentation search
Automating Communication Workflows
Mintive's Gmail MCP Server supports governed email workflows with centralized authentication, scoped tool access, and auditability.
Additional integrations include Outlook, Google Calendar, Notion, and Linear for comprehensive workflow automation.
Obot provides a broader platform catalog and registry model for MCP server discovery and deployment.
Governing Shadow AI: Visibility and Control Over LLM Tool Calls
Shadow AI, unauthorized or unmonitored AI tool usage, continues to grow as organizations adopt AI assistants. Organizations need visibility into what AI tools teams are using and what data they access.
Tracking Agent Activities in Real-time
Mintive's Gateway and Agent Monitor provide visibility across MCP traffic and local agent behavior:
- Monitoring of every MCP tool invocation
- Tracking of bash commands executed by coding agents
- Visibility into file operations and access patterns
- Real-time usage dashboards across supported AI clients
This addresses a critical gap: without monitoring, organizations have zero telemetry on AI agent behavior, no request history for security review, and uncontrolled access to sensitive systems.
Managing MCP Tool Inventories
Mintive provides:
- Complete inventory of installed MCPs across teams
- Permission tracking and usage pattern analysis
- Central registry of available MCP servers
- Virtual MCP Bundles exposing only minimum required tools
- Tool-update policy for admin approval or auto-enable rules when upstream tools change
Obot offers:
- Searchable catalog of community MCP servers
- Composite server creation for logical groupings
- Self-managed inventory tracking
Preventing Unauthorized Access and Commands
Mintive's security guardrails enable proactive protection:
- Block risky tool calls through rule-based policy
- Apply external DLP and guardrails integrations through Gateway Middleware
- Enforce data access policies through SSO, SCIM-driven RBAC, and tool-level allowlisting
- Alert on anomalous behavior patterns
Obot's security model relies on Kubernetes RBAC and customer-managed policy configuration, providing flexibility for experienced DevOps teams but requiring more setup effort.
Cost Management and Usage Analytics: Optimizing AI Spend
AI tool costs can escalate quickly without proper tracking. Both platforms approach cost management differently.
Mintive provides:
- Usage visibility across Claude, Cursor, ChatGPT, Gemini, Copilot, and other clients
- Centralized observability for MCP tool usage and agent activity
- Performance metrics to identify optimization opportunities
- Centralized credential management reducing key sprawl
Obot's model:
- OSS-first platform with no managed SaaS surfaced in the provided reference material
- Infrastructure costs, including Kubernetes cluster, storage, and networking, borne by organization
- Enterprise features and support terms should be validated directly with Obot
- Full cost transparency through self-hosted control
Total Cost of Ownership Analysis
The build vs. buy calculation favors managed platforms for many organizations:
Building equivalent infrastructure in-house:
- Upfront costs can be substantial once engineering, infrastructure, and compliance work are included
- Ongoing maintenance adds recurring engineering and operational cost
- Personnel: Dedicated DevOps resources for ongoing management
- Compliance: Independent audit and evidence-collection work
Mintive managed platform:
- Custom pricing based on team size
- Lower infrastructure overhead
- SOC 2 Type II audited controls included
- Managed connector hosting, uptime SLA details, and dedicated support options
Obot open-source:
- Software: Open source
- Infrastructure: Kubernetes cluster operational costs
- Compliance: Customer-managed
- Support: Validate enterprise support and SLA terms directly with Obot
For organizations prioritizing compliance and deployment speed, Mintive's managed approach can deliver faster time-to-value despite licensing costs.
Developer Experience: Enabling Innovation Without Compromise
Developer adoption depends on workflow integration and friction reduction.
Seamless Integration with Popular AI Clients
Mintive supports governance for:
- Claude
- Cursor
- ChatGPT
- Gemini
- Microsoft Copilot
- Custom MCP-compatible agents
Obot supports:
- Claude
- Cursor
- VSCode
- Custom agents through API
Mintive's Cursor Hooks Partners Program listing provides validated integration for coding agent monitoring.
Self-Service Access for Faster Development
Mintive enables:
- Developers request and receive AI tool access through governed workflows
- Pre-configured policies reduce security review delays
- No changes required to existing developer workflows
- Works with existing AI tool deployments
Obot's developer experience depends on organizational Kubernetes expertise:
- GitOps workflows appeal to platform engineering teams
- Full infrastructure control enables deep customization
- Steeper learning curve for teams new to Kubernetes
Centralized Credential Management
Mintive centralizes:
- AI tool API keys and tokens in one place
- Shared and per-user authentication configurations
- Service account management at admin level
- Individual OAuth flows when needed
- Agent Bundles with M2M auth, independent rotation and revocation, and “act as agent” flows for connectors that require per-agent OAuth
This eliminates credential sprawl, a common security risk when teams manage API keys independently.
From Local to Enterprise: Scaling MCP for Production
The path from local MCP experimentation to production deployment reveals fundamental differences between platforms.
Transforming Local Servers into Production-Ready Services
Most MCP servers are STDIO-based, designed for local execution. Enterprise deployment requires:
- Remote accessibility without local installations
- Authentication wrapping for security
- Monitoring and logging for compliance
- High availability for production SLAs
Mintive approach:
- Host MCP connectors on Mintive-managed infrastructure
- Provide OAuth brokering for stdio and hosted MCP servers
- Apply SSO, SCIM-driven RBAC, and tool-level policy through the gateway
- Include production monitoring, logging, and centralized observability
Obot approach:
- Deploy to customer-managed infrastructure
- Configure Docker and Kubernetes workflows
- Authentication setup through customer-managed identity and policy controls
- Monitoring through Kubernetes-native tools
Mintive can reduce authentication setup and runtime operations compared to more manual approaches.
Ensuring Enterprise SLAs and High Availability
Mintive provides:
- Uptime SLA details through the Trust Center and security review process
- Managed connector hosting and runtime operations
- Latency depends on deployment architecture, traffic patterns, and policy configuration
Obot requires:
- Validate SLA and enterprise support terms directly with Obot
- Self-managed failover configuration
- Manual regional setup
- Performance dependent on Kubernetes cluster configuration
Global Deployment with Data Residency
For multinational organizations, data residency controls matter:
Mintive offers:
- Managed SaaS-first deployment with US and EU options
- Data residency options available through enterprise review
- Audit trails and security documentation for regional requirements
Obot enables:
- Self-hosted deployment in any region
- Air-gapped options for maximum control
- Customer-managed compliance documentation
Why Mintive Delivers for Enterprise AI Governance
Organizations evaluating MCP gateways face a fundamental choice: managed compliance and governance or self-hosted infrastructure control. Mintive addresses the core enterprise requirements that determine AI deployment success.
For regulated industries, Mintive is SOC 2 Type II audited, compliant with HIPAA standards, penetration tested, and built with complete audit trails. Customers handling protected health information can request HIPAA documentation, and Mintive signs BAAs. Trust Center documentation helps security teams review the platform's controls during procurement.
For engineering teams, managed SaaS-first deployment, hosted MCP connectors, OAuth brokering, and Admin MCP reduce the setup cycles required for self-hosted Kubernetes configurations. Lower infrastructure overhead frees DevOps resources for higher-value work, enabling teams to focus on building AI applications rather than managing gateway infrastructure.
For security teams, SSO, SCIM-driven RBAC, Virtual MCP Bundles, Agent Bundles, tool-level allowlisting, rule-based policy, complete audit trails, and Agent Monitor provide the visibility and control required before connecting AI agents to sensitive systems. The ability to track MCP tool invocations, bash commands, file operations, and prompt submissions addresses the shadow AI challenge that affects organizations adopting coding agents and AI assistants at scale.
For finance teams, predictable pricing with included security and governance features can deliver lower total cost of ownership than open-source alternatives when accounting for the full burden of infrastructure management, personnel requirements, and compliance program costs. The managed platform model reduces operational complexity that can drive up self-hosted TCO over time.
Mintive transforms MCP from a developer utility into production-grade enterprise infrastructure. From local MCP to enterprise deployment: fast, secure, and governed.
Book a demo to see how Mintive can accelerate enterprise AI governance.
Frequently Asked Questions
What is the difference between an MCP Gateway and an API Gateway?
An API gateway manages traditional REST/GraphQL API traffic with rate limiting, authentication, and routing. An MCP gateway specifically handles Model Context Protocol traffic, the standardized way AI assistants connect to tools and data sources. MCP gateways address unique requirements like tool-call tracking, AI-specific audit trails, and converting local STDIO servers to remotely accessible services. While API gateway vendors are adding MCP support, Gartner's 2025 Software Engineering Survey projects that 75% will do so by 2026; dedicated MCP gateways like Mintive provide deeper functionality for AI-specific governance.
How does Mintive ensure privacy and compliance for enterprise AI?
Mintive is SOC 2 Type II audited, with continuous compliance monitoring via Drata. Enterprise SSO, complete audit trails, PII detection, role-based access control, and tool-level policy are built into the platform. Mintive is compliant with HIPAA standards, customers handling protected health information can request HIPAA documentation, and Mintive signs BAAs. Data is encrypted in transit and at rest, and data residency options are available through enterprise review. For detailed security documentation, visit Mintive's Trust Center.
Can Mintive integrate with my existing data sources and LLM clients?
Mintive supports governance for major AI clients including Claude, Cursor, ChatGPT, Gemini, Microsoft Copilot, and custom MCP-compatible agents. Hosted MCP connectors provide integration with Snowflake, Elasticsearch, Gmail, PostgreSQL, MongoDB, and other enterprise systems. The platform provides a central registry of available MCP servers with governed configuration. Custom connectors can be deployed through Admin MCP and Mintive tooling.
What specific security features does Mintive offer for coding agents?
Mintive's Agent Monitor and Gateway governance monitor MCP tool invocations, bash commands, file operations, and prompt submissions from coding agents like Cursor and Claude Code. Security guardrails can block risky tool calls, apply rule-based policy, integrate with external DLP and guardrails tools, and provide complete audit trails for security review. The platform tracks installed MCPs, monitors usage patterns, and enables policy enforcement without disrupting developer workflows.
How does Mintive help organizations manage the cost of AI?
Mintive provides centralized usage visibility across supported AI clients and MCP tools. Centralized credential management reduces key sprawl and associated security risks. Compared to building equivalent infrastructure in-house, which can become expensive once engineering, infrastructure, and compliance work are included, Mintive's managed platform reduces infrastructure overhead while providing security, governance, and observability capabilities through a managed deployment model.